 Pharova
Decides real or noise, for every alert
- Checks every indicator against your threat intelligence
- Reads the rule's 30-day history and related alerts
- Closes clear noise under strict rules, with a daily human spot check
about 10 s per alert
Pharova is a team of AI security analysts that works on top of the tools you already own. It triages every alert, investigates the ones that matter, prepares the response in the right tool and tells your team exactly what is left to do.
Speed figures are expected averages, measured from when Pharova receives an alert. Targets: 95% of alerts triaged within 30 seconds and investigated within 2 minutes.
Hunt for threats and build detection rules in plain words. Pharova understands about 20 kinds of security hunt, hundreds of tool names and nicknames, and typos. When it cannot see something, it says so instead of quietly finding nothing.
Pick an example:
Hundreds to thousands of alerts a day, most of them false positives or routine admin work. Every real investigation means pivoting across four or five consoles, and one analyst seat around the clock takes about five people.
about 10 s per alert
about 1 min per investigation
you approve, Pharova does the rest
Looks back over weeks of history for what no single alert shows. Ask in plain words, such as "anything dumping LSASS".
Related alerts become one case with a clear story and plan, kept in step both ways with ServiceNow or Jira.
Daily to quarterly reports for security leads and management, written from the numbers only.
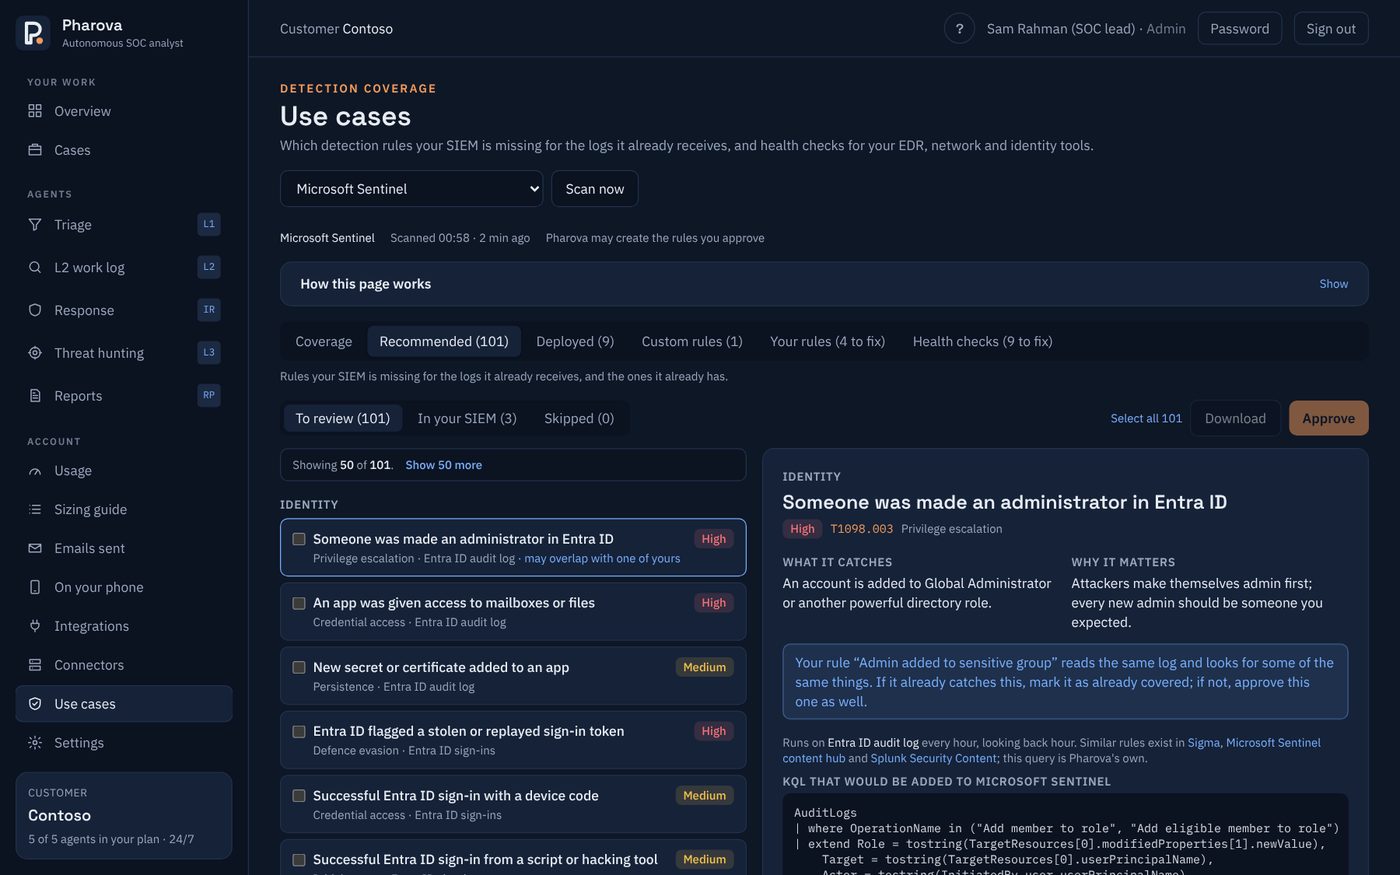
Pharova connects to your SIEM, sees which log sources you already have, and suggests the detection rules you are missing. Approve them and Pharova creates them in your SIEM for you.
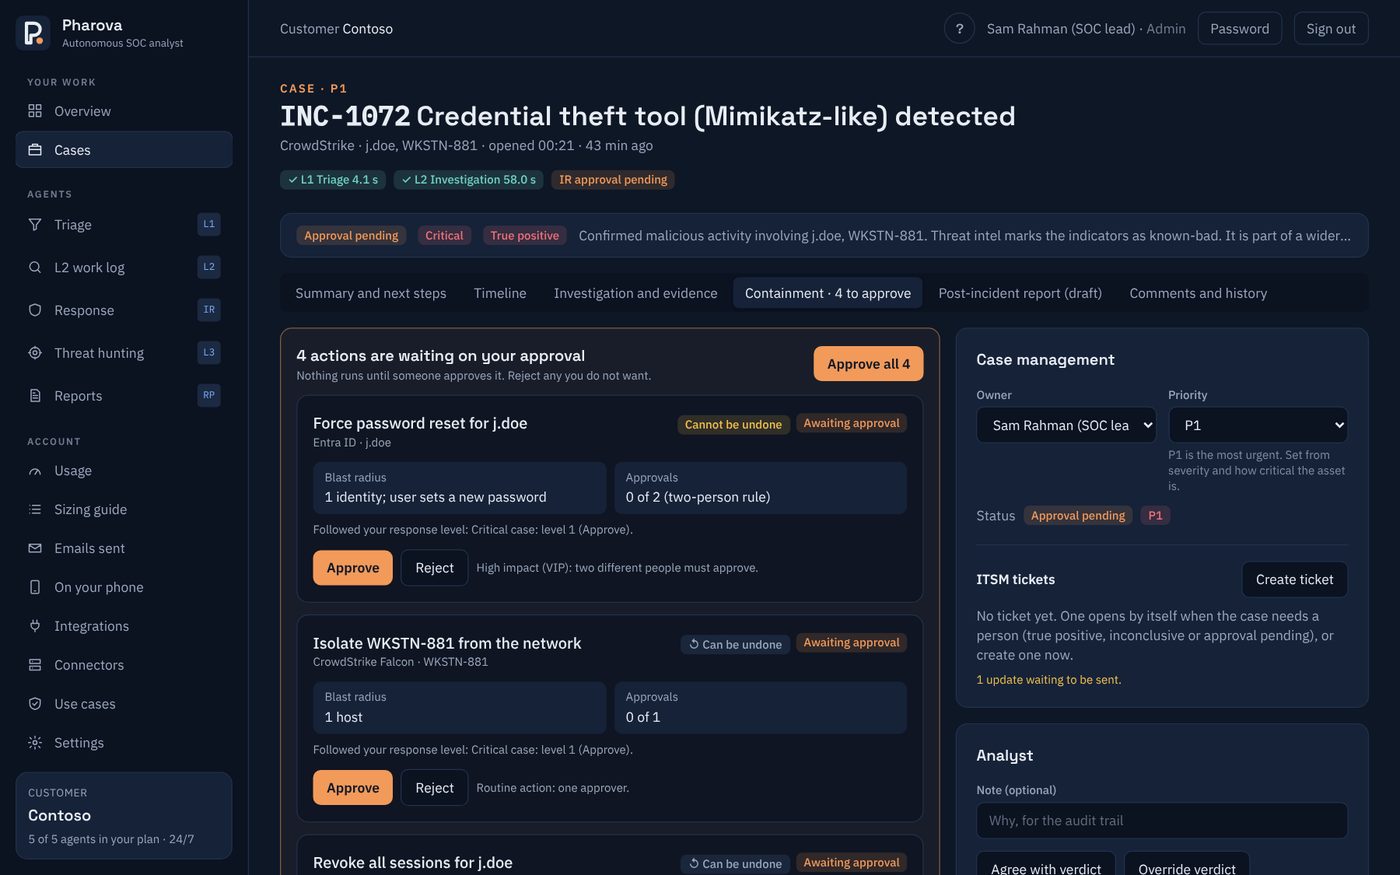
Choose how far Pharova may go, for all cases or for each severity. Approvals happen only inside Pharova, on the web or on your phone, never from an email link.
With the Privacy Gateway option, machine names, internal addresses and company names are replaced with stand-ins inside your network, before anything reaches Pharova. Investigations work the same, and the real names come back when Pharova acts in your tools.
With Arabic findings, each case carries a short brief written in Arabic from the case facts, so teams and management can read what happened and what to do in their own language. Technical details stay exactly as your tools give them.
Seven SIEMs, the major EDR and XDR platforms, identity, email, firewalls, threat intelligence and your service desk. Each one has a guided setup card that tests the connection before anything is switched on.
We connect to a copy of your tools in a guided session and show you every decision, with the evidence behind it.